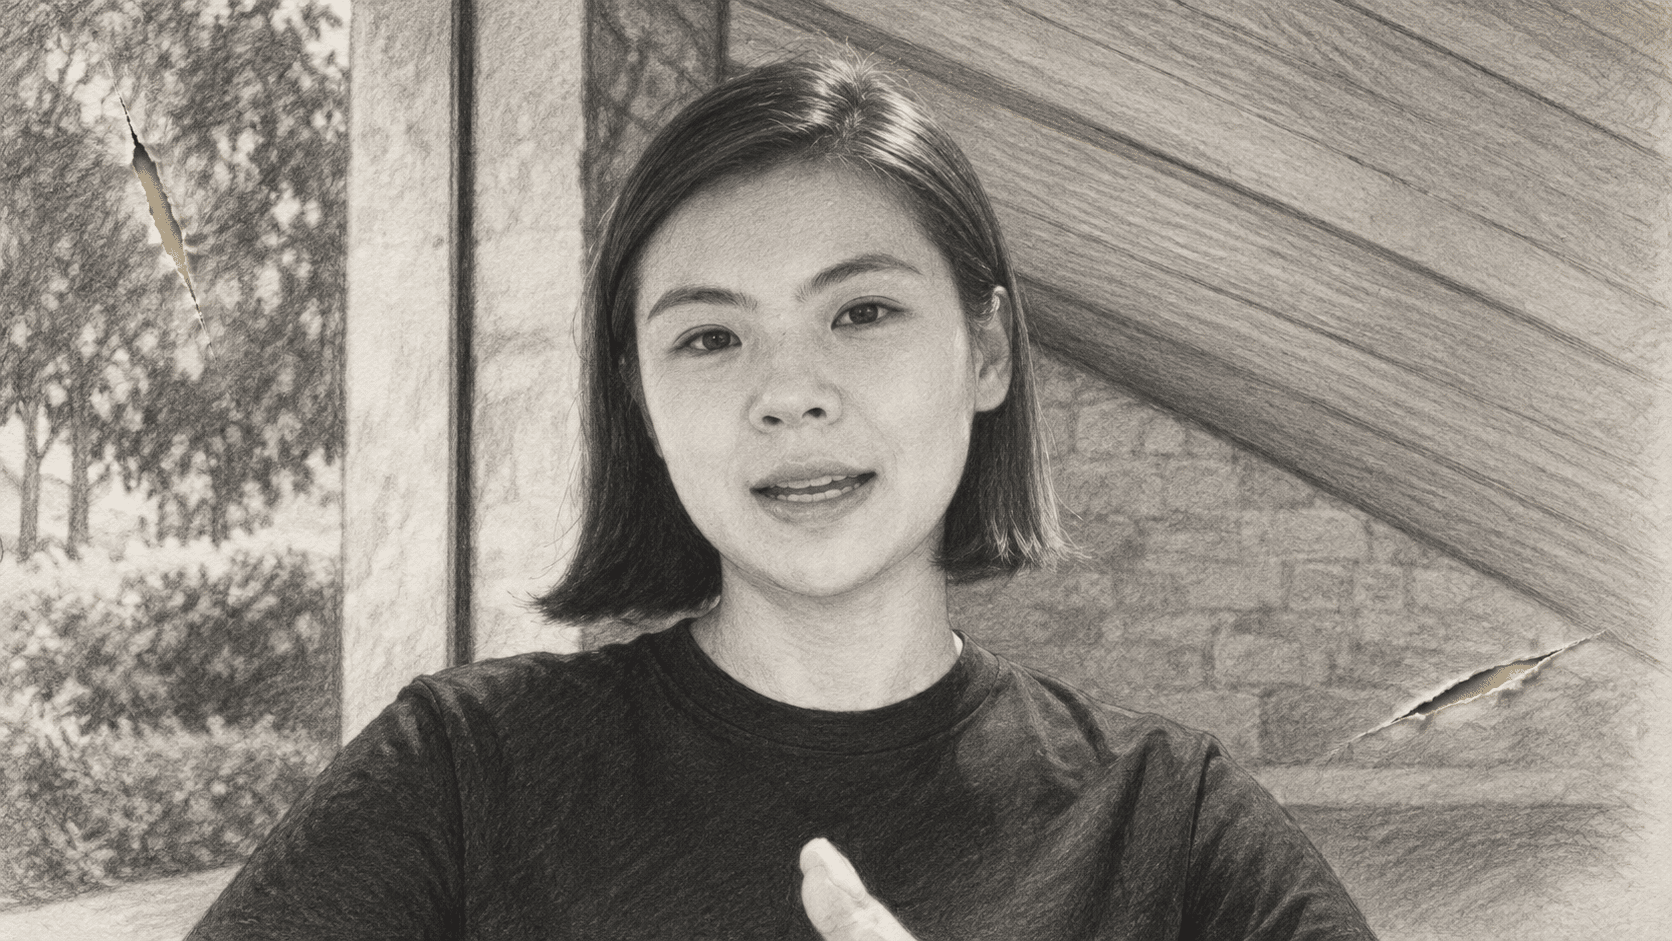
Bitget CEO Gracy Chen said scammers impersonating a major investment firm targeted her on Monday, four days after attackers took about $387.5 million from the exchange.
Chen said on the show Tuesday that the attempt was “not a hack” but “a social engineering towards me,” and that “it happened yesterday.”
Chen said the impostors knew she was talking with many outside partners and looking for help after the theft. Because several people at the firm are well known, “they actually formed a team,” she said, with each member playing a different role, asking Bitget to do things or offering help. Chen said Bitget nearly began a real conversation with the group before she checked with the firm’s leader, whom she already knew, through a separate channel and learned the approach was fake. She did not name the firm.
Asked by host Laura Shin whether North Korean hackers were behind it or ordinary scammers, Chen said, “it could be both.”
Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter.
What Bitget Has Said About the Theft
Chen said on the show that the attackers used a previously unknown flaw in a security product from an outside vendor to reach an internal management system, then sent fake withdrawal commands to Bitget’s wallets. She declined to say whether social engineering played a part in the theft itself, and said Bitget will publish an incident report.
Bitget put the loss at $387.5 million on Friday, as Unchained reported. Chen said the same day that the attack “is consistent with techniques used by DPRK-linked hacker groups.” She has since said that statement was based on “preliminary indicators” that are still being assessed and “should not be treated as a definitive attribution.”
Chen’s Warning to Other Teams
Chen said attackers study the industry’s public figures and pose as the people those figures are likely to contact. “They know I do a lot of interviews, they know I talk to a lot of external partners,” she said.
She said a request to do an interview on an unfamiliar livestreaming platform, rather than the Google Meet or Zoom a person normally uses, is a warning sign. “I think this is highly suspicious,” she said.
For exchanges and protocols that hold user funds, Chen said teams should check “every single possibility that you can be exploited.”
Related Listen: I Went Undercover to Interview a North Korean Crypto Hacker