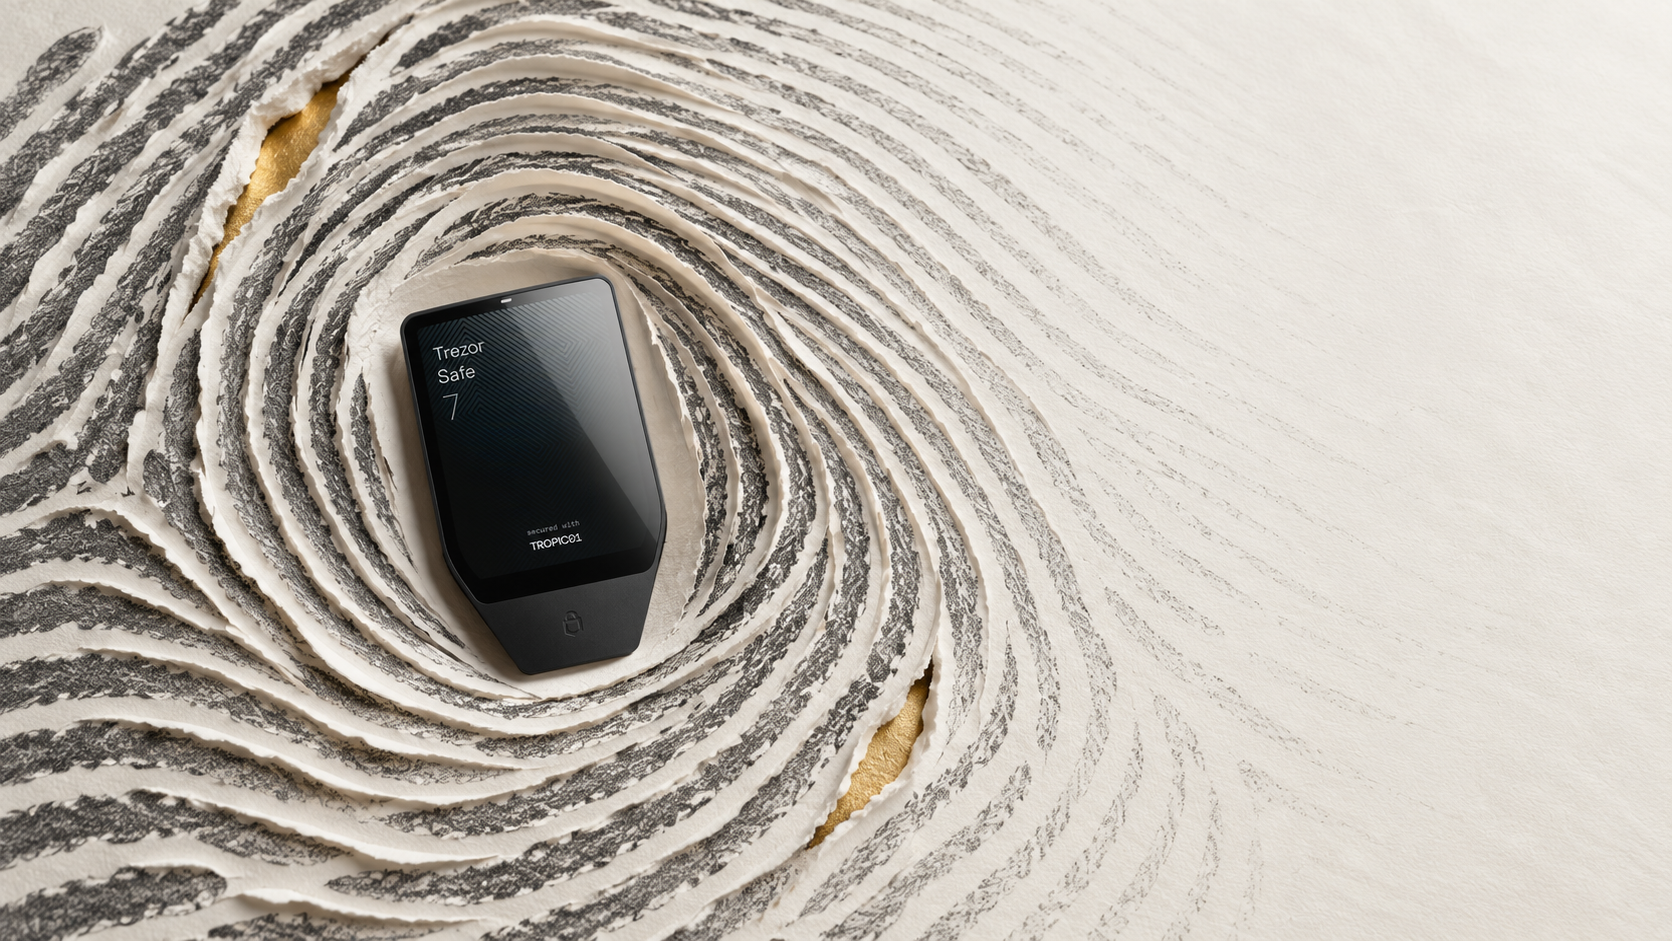
Hardware wallet maker Trezor is shrinking the list of resellers allowed to sell its devices, the company announced on X on Tuesday, pointing to “recent supply-chain incidents” as the reason.
A smaller network, Trezor said in the post, lets it “more effectively check those we work with.” The post did not give a number of resellers being dropped, name any of them, or set a date for the change.
“Let us be very clear: there is not a single piece of evidence that Trezor devices have been compromised,” the company wrote. It described the decision as “a preventive step, taken out of an abundance of caution,” and thanked its sales partners “for the years of work putting Trezor in people’s hands.”
Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter.
What Came Before
Trezor did not say which incidents it had in mind, and Tuesday’s post does not mention any other company or reseller.
The announcement came four days after rival wallet maker Ledger opened an investigation into drained wallets traced to devices sold in Southeast Asia by the reseller CryptoBilis. Ledger said on Oct. 9 it had asked CryptoBilis to pause sales and shipments of Ledger devices, and said later that one affected user’s device contained an unauthorized hardware implant. Onchain analysts have put the losses at about $93 million to more than $103 million. Ledger has not confirmed a total.
Trezor said in a reply on X on Monday that CryptoBilis was off its reseller list and that Trezor sales through it had stopped, adding: “We have no reports of tampered Trezors from CryptoBilis.”
Trezor’s Vendor Breaches
Trezor has also handled two breaches at outside vendors this year, neither of them a reseller. In August, it disclosed unauthorized access at its shipping provider, ShipMonk, and a September update raised the count of affected customers to 80,689. In September, a breach at email provider Brevo exposed roughly 347,000 newsletter addresses, which attackers then used to send a phishing email. In both cases, Trezor said its own wallets and systems were not affected.
Related Listen: Bits + Bips: Is Any Cold Wallet Safe? Inside the Coldcard Hack’s Wave Three